Your cryptographic architecture may be secure digitally. But who can physically access the hardware?
From Digital to Physical: Securing Cryptographic Infrastructure
A well-designed cryptographic environment can include HSMs, PKI infrastructure, key-management systems, secure servers and increasingly post-quantum cryptography platforms.
Considerable attention goes into protecting keys and controlling logical access.
But when designing the complete solution, integrators should ask one additional question:
How is physical access to the cryptographic hardware controlled?
Physical Security as Part of Defence in Depth
A standard 19-inch rack server cabinet is primarily designed to organize IT equipment, not to provide certified resistance against physical attack.
Kaso’s existing guidance highlights this distinction: conventional lightweight server cabinets may provide practical housing but comparatively little protection against determined physical access.
For environments containing sensitive cryptographic equipment, the enclosure itself can therefore become part of the security architecture.
A Certified Security Boundary Around Standard 19-Inch Rack Equipment
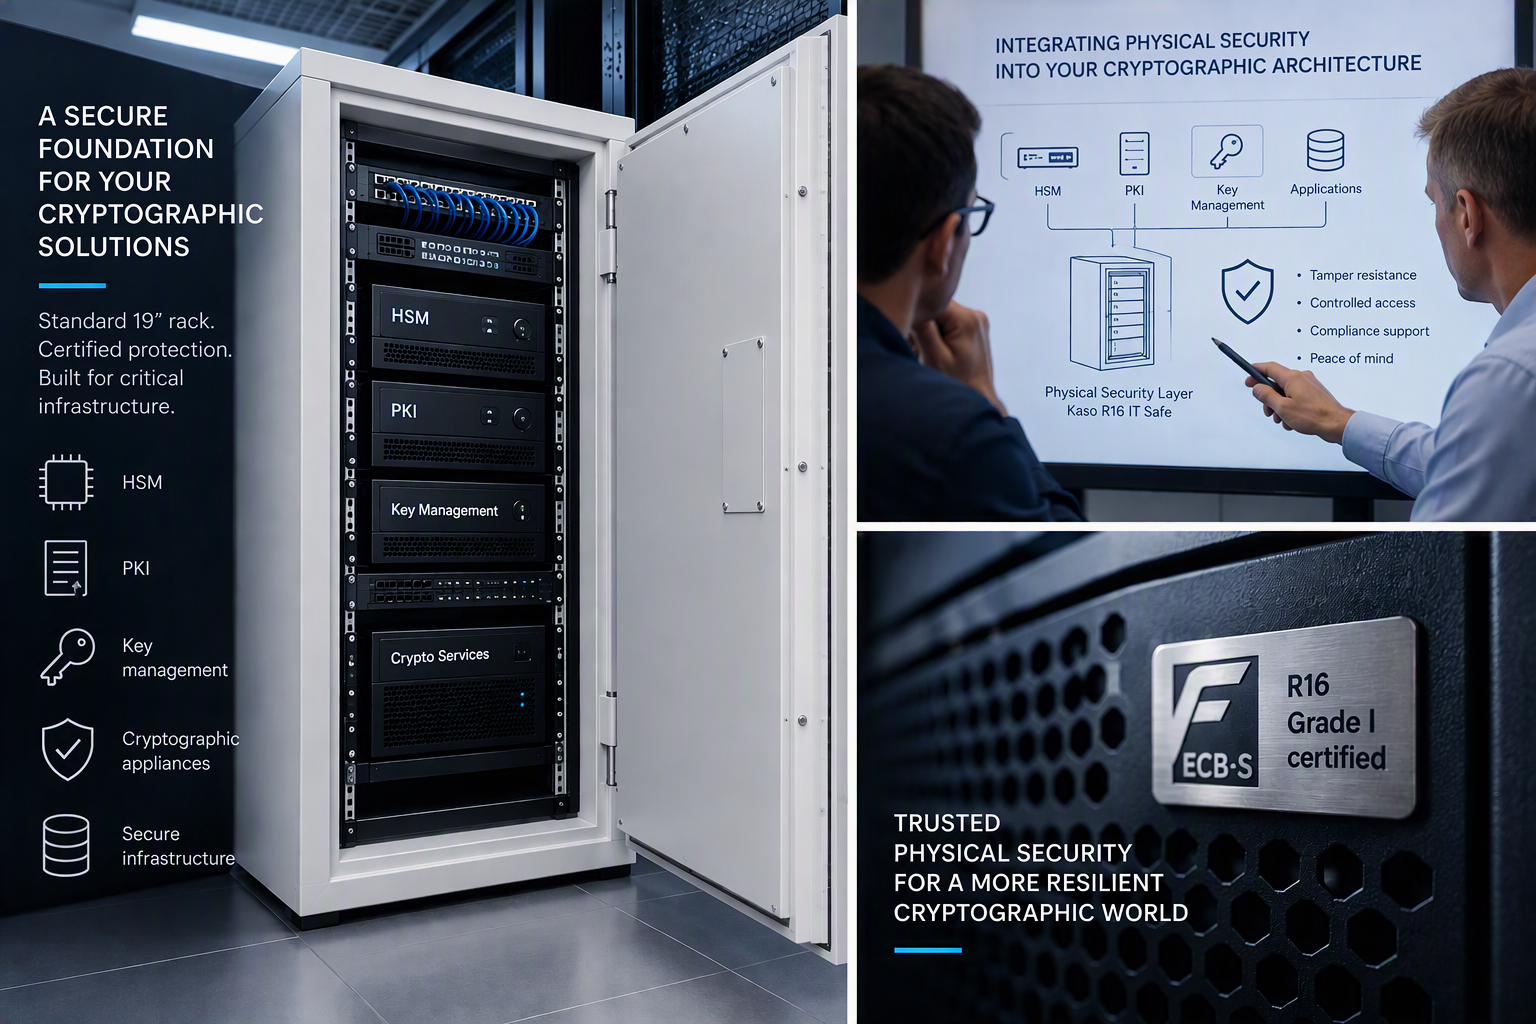
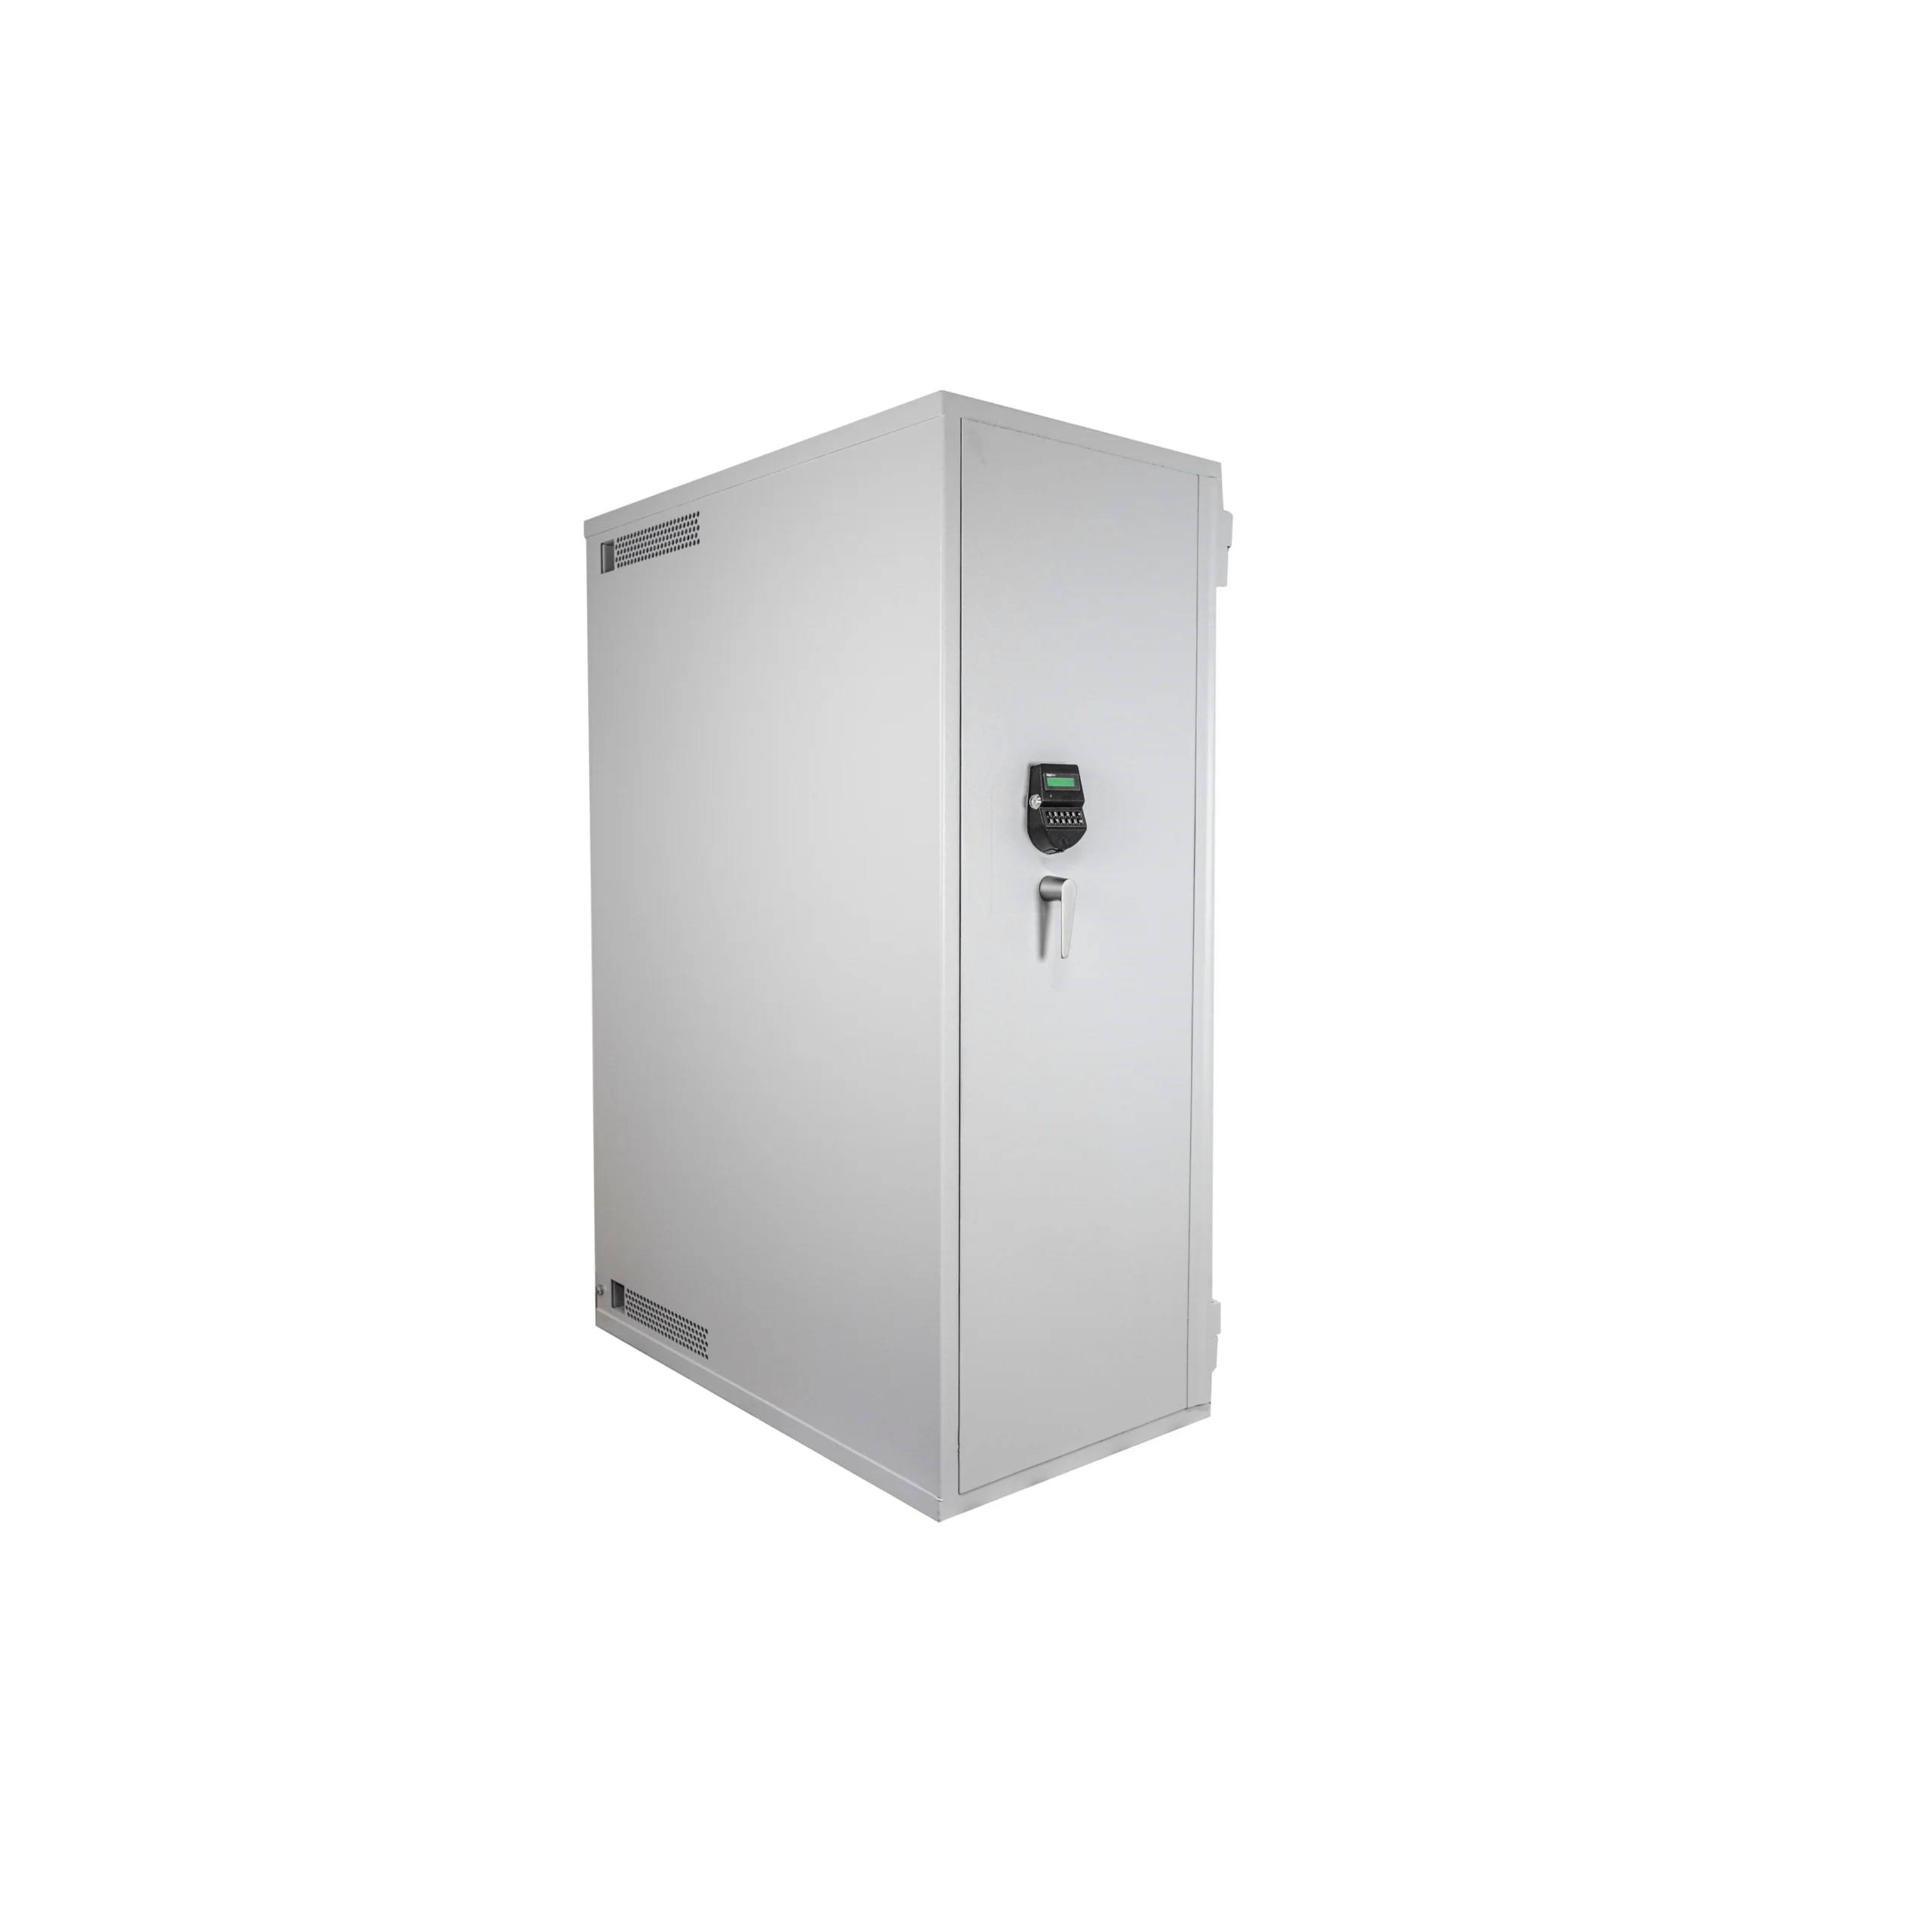
The Kaso R16 IT Safe provides a standard 19-inch rack inside an ECB-S R16 Grade I certified enclosure. It combines physical protection with active ventilation, cable routing and rack-mount compatibility.
Instead of designing an entire high-security room around a relatively small amount of critical equipment, an integrator can therefore consider protecting the equipment itself.
This can be particularly interesting for:
- HSM installations
- PKI infrastructure
- Key-management servers
- Certificate authority infrastructure
- Cryptographic appliances
- Sensitive authentication systems
- Post-quantum cryptography infrastructure
Integrating Physical Security into the Solution
For a cryptography integrator, physical protection does not need to be a separate project.
The R16 provides a familiar 19-inch rack installation environment, with a removable, depth-adjustable rack and thermostatically controlled active ventilation. Multiple locking and external alarm/management options are available to address various physical-access and management policies.
The result is a straightforward principle:
Secure the cryptography digitally. Secure the hardware physically.
One More Layer for High-Security Architecture
When the infrastructure being protected contains an organization’s most sensitive cryptographic keys, physical access deserves the same systematic consideration as logical access.
Adding a certified physical enclosure enables HSM, PKI and cryptography integrators to offer customers another layer of protection without abandoning standard 19-inch rack hardware.
Add certified physical protection to your next cryptographic infrastructure project.
Explore Kaso R16 IT Safes: R16 High Security 19-inch rack Server Rack Cabinet