Physical Security for HSM Hardware Security Modules
Hardware Security Modules are designed to protect some of an organization’s most valuable digital assets: cryptographic keys.
HSM security is typically considered from the perspective of cryptography, authentication and tamper resistance. But there is another layer that should not be overlooked:
Physical access to the infrastructure hosting the HSM.
For organizations operating high-value cryptographic environments, controlling who can physically access, disconnect or remove critical equipment can be an important part of the overall security architecture.
Adding a Physical Security Layer Around the HSM
One approach is to install HSM equipment inside a dedicated high-security IT enclosure.
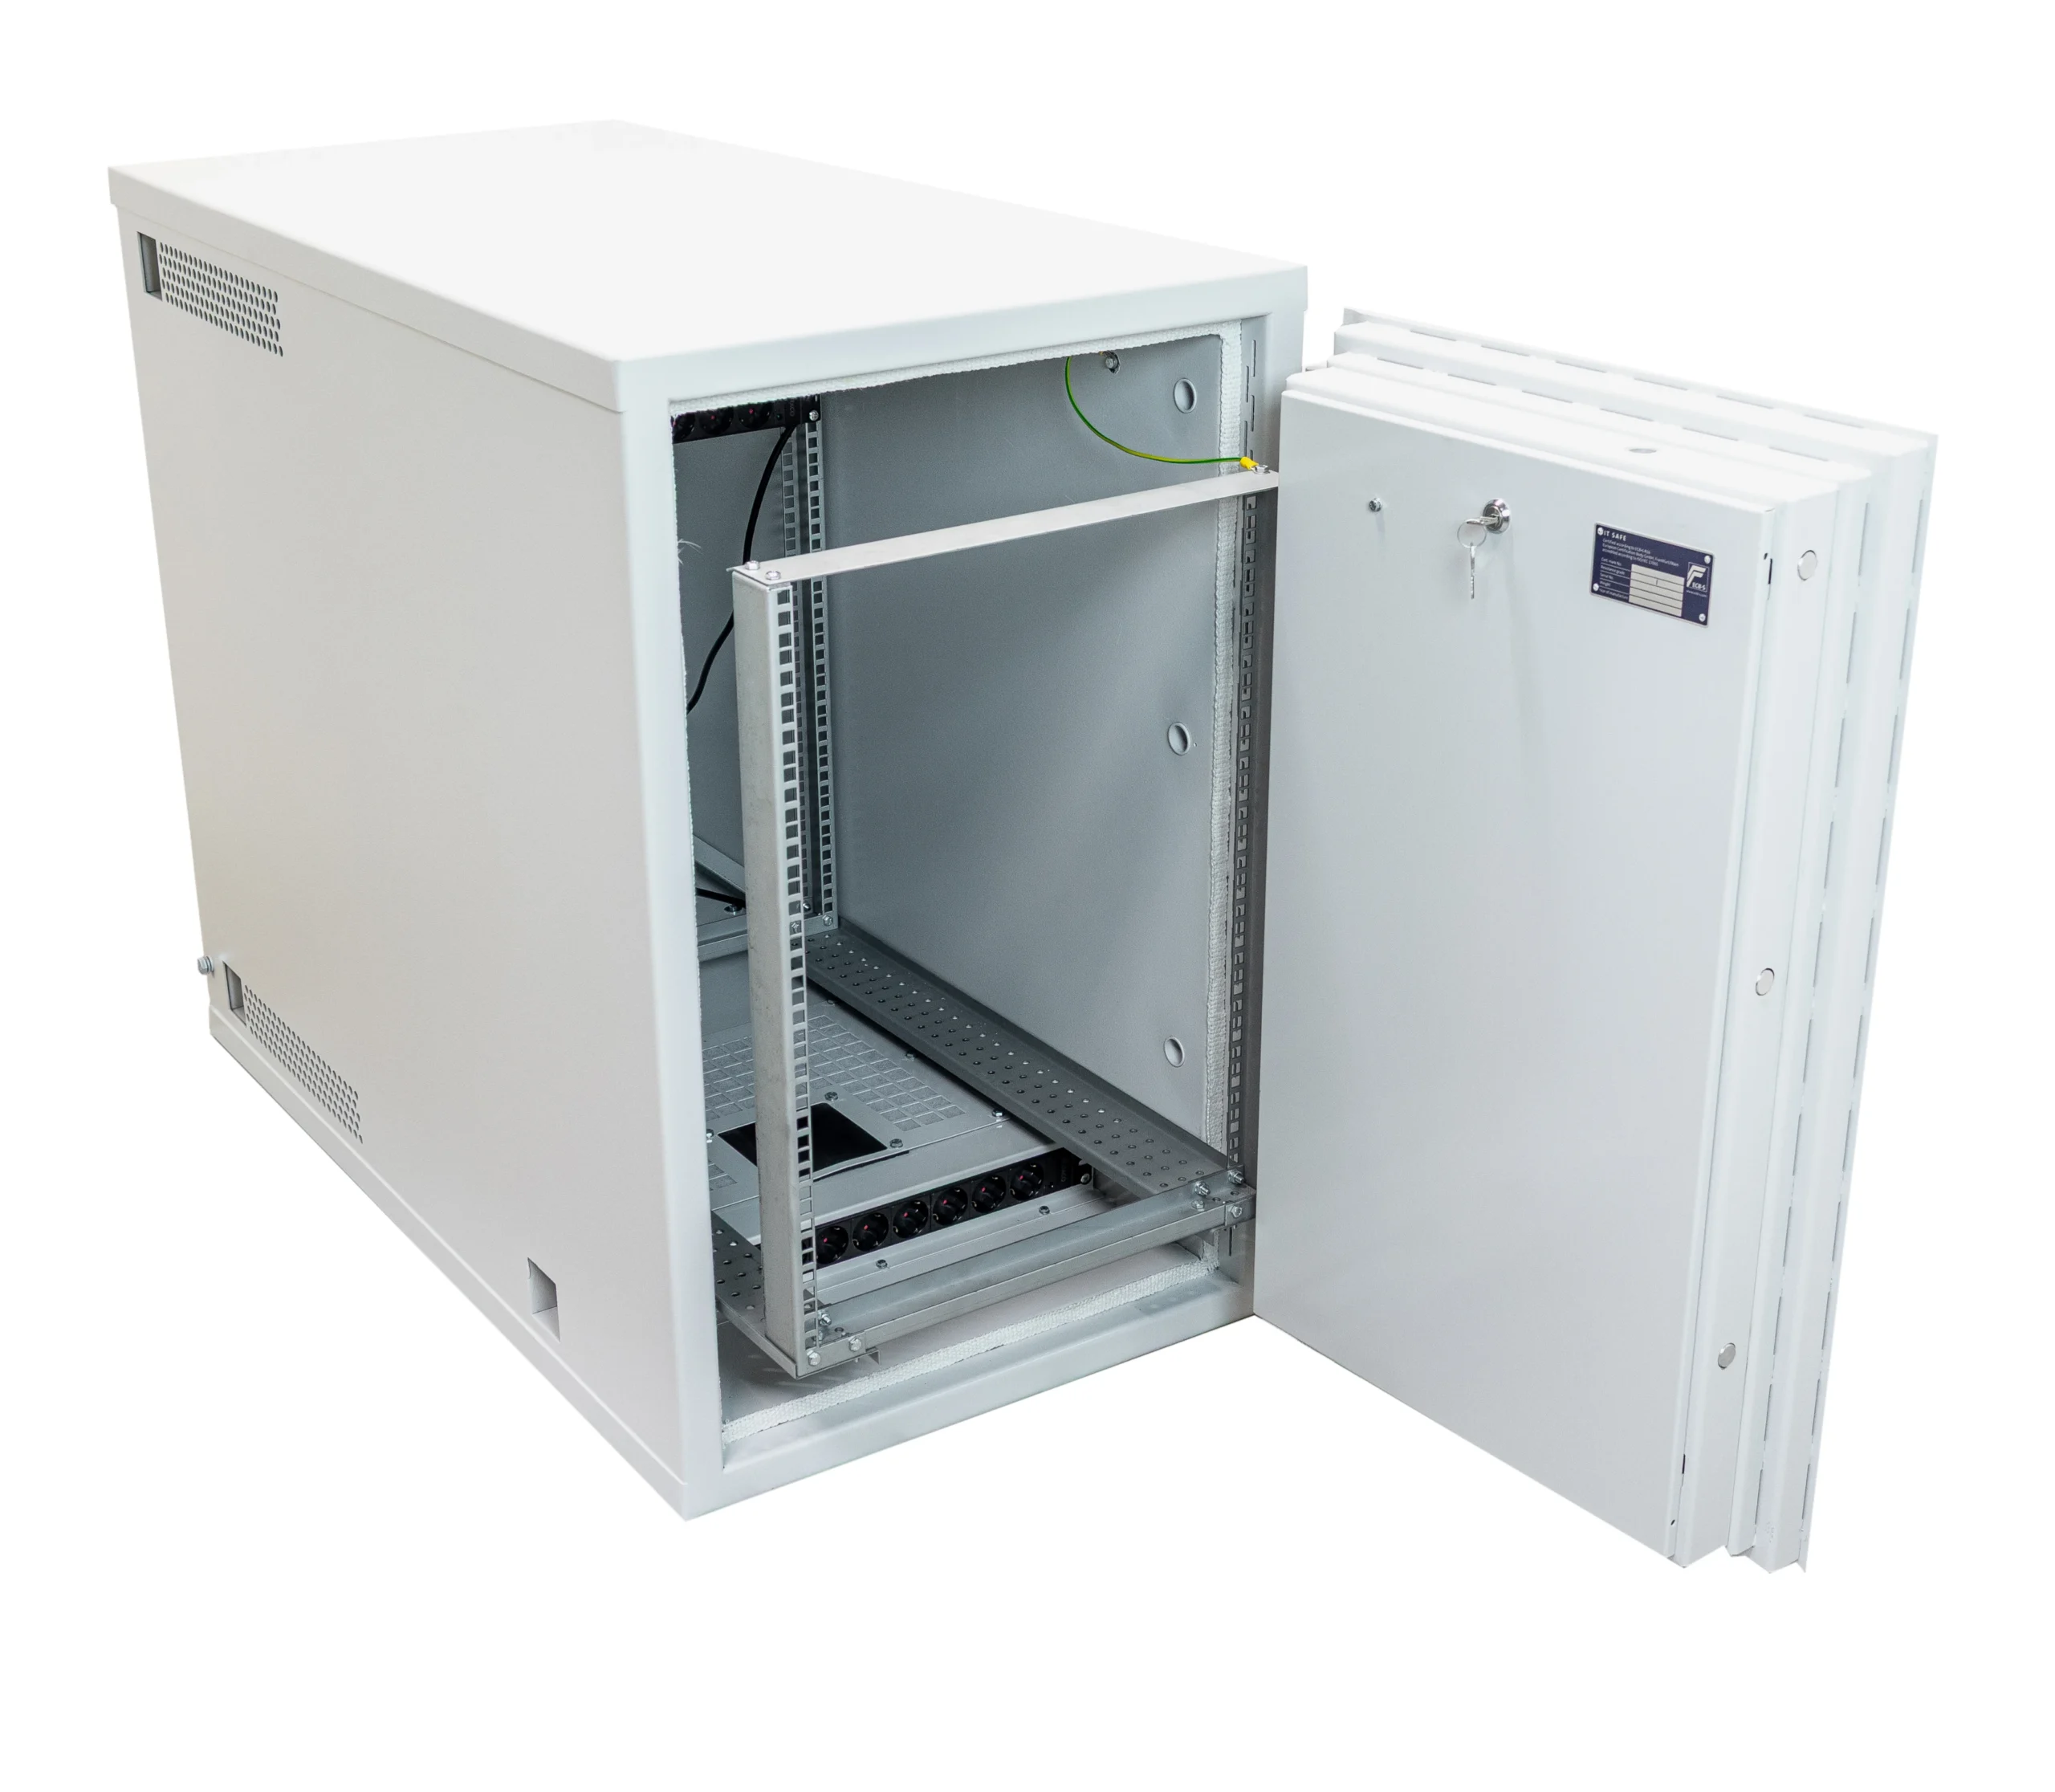
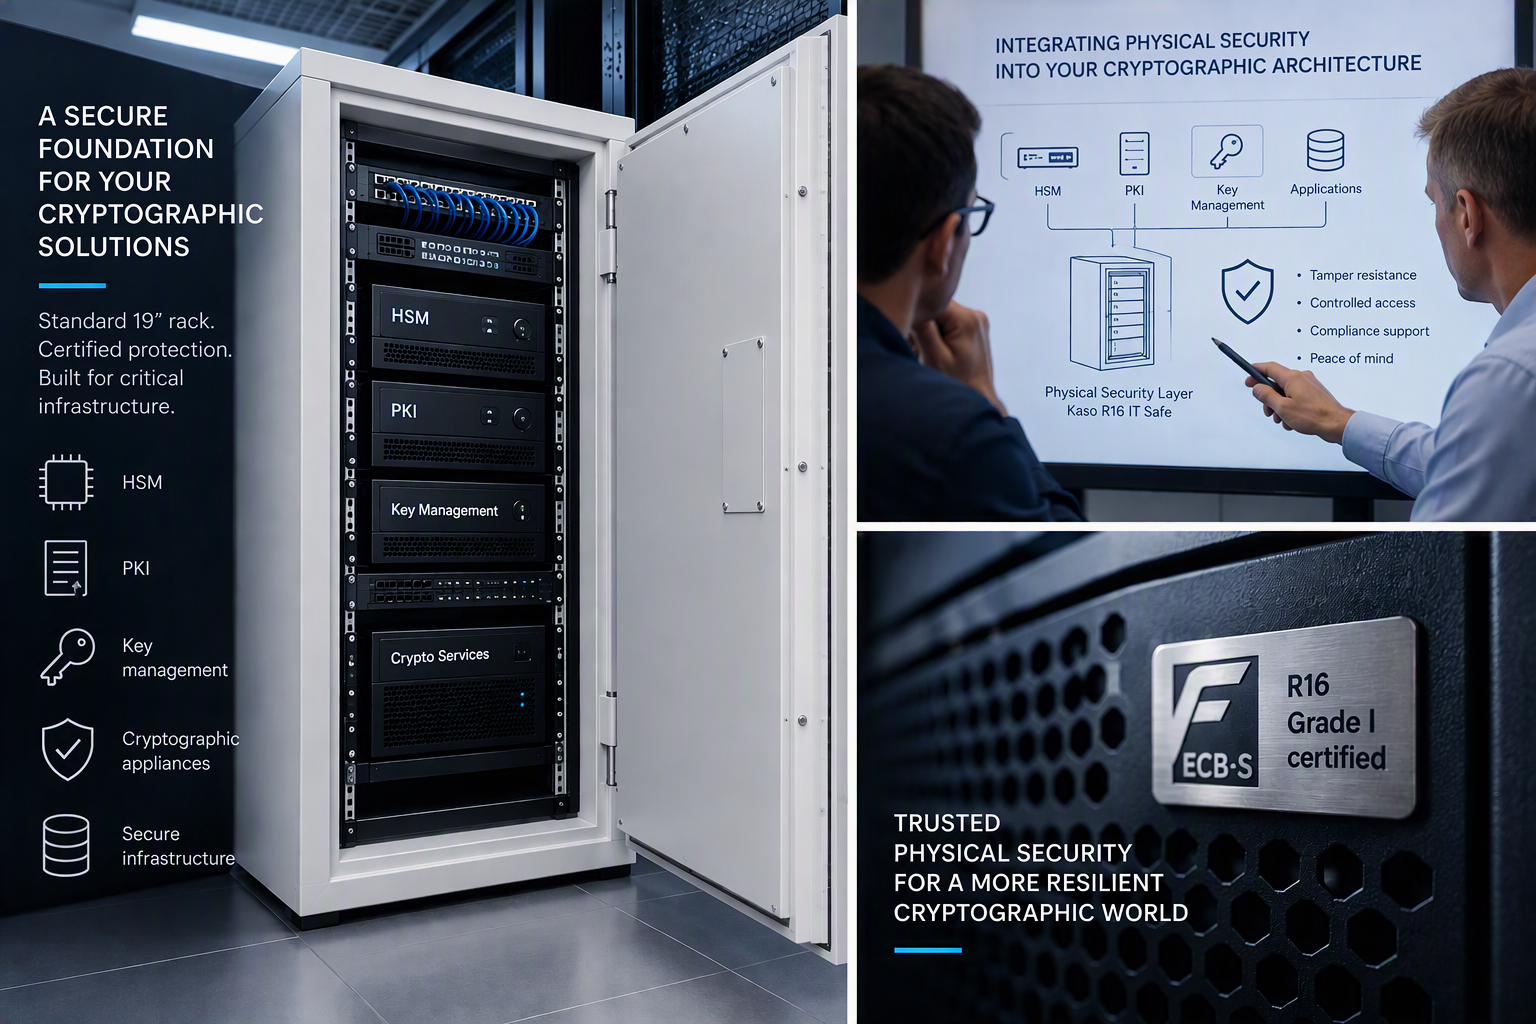
The Kaso R16 IT Safe combines a standard 19-inch IT environment with certified burglary resistance. R16 IT Safes are certified according to ECB-S R16 Guidelines to Grade I and are specifically intended for protecting sensitive IT and cryptographic hardware.
This creates an additional physical security boundary around the HSM without requiring a completely separate secure room.
Designed for 19-Inch Cryptographic Equipment
Security cannot come at the expense of normal IT operation.
The R16 includes a depth-adjustable, pull-out 19-inch rack, active thermostatically controlled ventilation and dedicated cable entries. Available configurations cover rack heights from 6U to 34U.
This makes it possible to house sensitive rack-mounted equipment while maintaining cooling, cabling and serviceability.
Controlled Physical Access
Access to cryptographic equipment may also require stricter procedures than access to ordinary IT hardware.
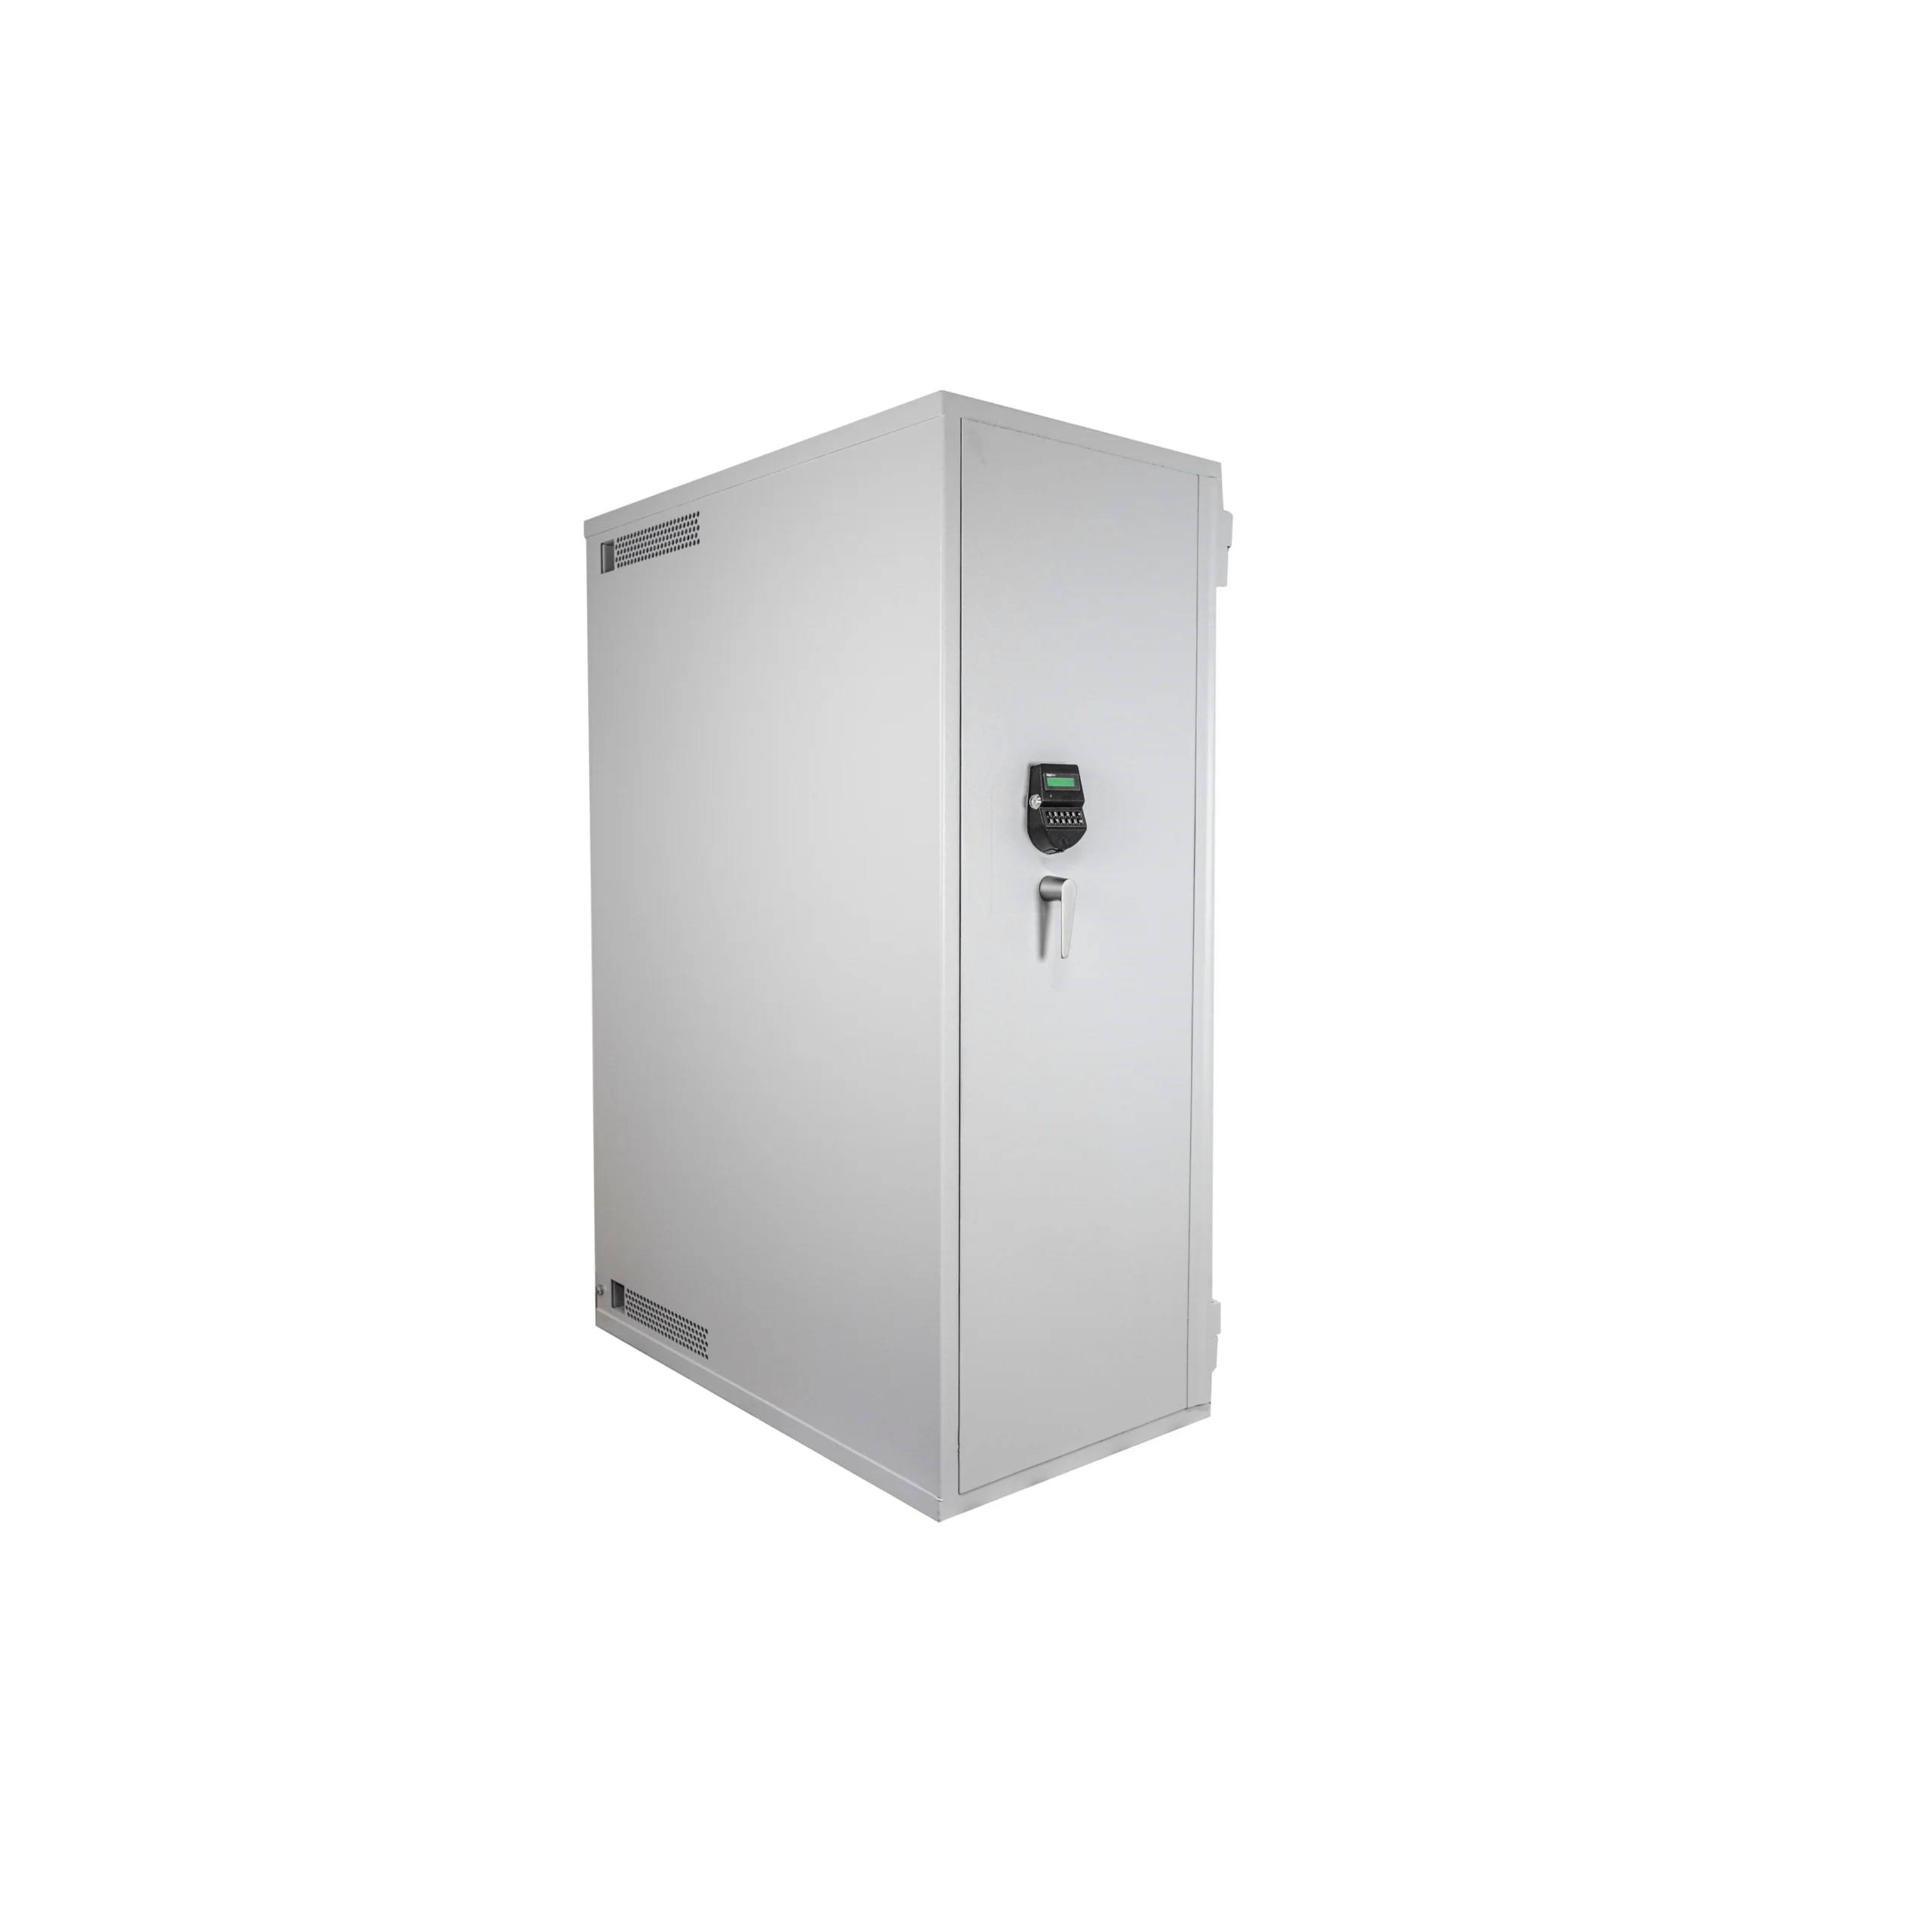
The R16 can be configured with EN 1300 certified electronic or mechanical locking systems, including multiple-lock configurations. Additionally R16 IT safes are also available with time-delay, time-lock, multi-user control and remote monitoring/management options.
For HSM manufacturers, this creates an opportunity to complement the HSM’s internal security architecture with a certified external physical protection layer.
Protect the Keys. Protect the Hardware.
Cryptographic security does not stop at the HSM enclosure.
Where additional protection against physical access, manipulation or removal is required, a certified IT safe can become another layer in a defence-in-depth architecture.
See how the Kaso R16 can protect HSM and cryptographic infrastructure.
Explore Kaso R16 IT Safes: R16 High Security Server Rack Cabinet